BlindCell is an advanced, security- and privacy-focused text encryption and messaging application for iOS and Android mobile phones and smart devices, developed by Experts for Integrated Solutions Ltd. BlindCell enables users to encrypt, exchange, and share secure text messages through popular social media and messaging applications, including WhatsApp, Viber, Messenger, and other social media applications, as well as SMS messaging applications and public or private email services. Unlike conventional messaging solutions, BlindCell applies the standard Advanced Encryption Standard (AES-256) encryption directly on the user's device, using locally generated, recipient-specific secret keys that are never exchanged or transmitted between users or through third-party services.
The recipient's mobile number is used as an identifier in the key-generation process, providing an additional layer of protection independently of the communication platform. Designed to meet the growing demand for security and privacy in digital communication, BlindCell empowers individuals, professionals, businesses, and organizations to protect their confidential messages and sensitive information with confidence, flexibility, and ease of use.
Empowering Messaging Security & Privacy
Developing projects from concept to execution through feasibility assessment, planning, coordination, scheduling, cost control, risk management, and overall project supervision.
Providing integrated Engineering, Procurement and Construction services to deliver projects efficiently, safely, and in accordance with agreed technical, quality, cost, and schedule requirements.
Supporting the reliable and efficient operation of facilities and systems through planned operation, preventive and corrective maintenance, performance monitoring, and technical support.
Providing independent technical, commercial, and strategic advice to support project planning, technology selection, decision-making, performance improvement, and problem solving.
Sourcing and supplying equipment, systems, materials, technologies, and spare parts from qualified manufacturers and suppliers to meet project and operational requirements.
Delivering professional training, technical workshops, and tailored capacity-building programmes to develop skills, strengthen organisational capabilities, and support knowledge transfer.
Developing projects from concept to execution through feasibility assessment, planning, coordination, scheduling, cost control, risk management, and overall project supervision.
Providing integrated Engineering, Procurement and Construction services to deliver projects efficiently, safely, and in accordance with agreed technical, quality, cost, and schedule requirements.
Supporting the reliable and efficient operation of facilities and systems through planned operation, preventive and corrective maintenance, performance monitoring, and technical support.
Providing independent technical, commercial, and strategic advice to support project planning, technology selection, decision-making, performance improvement, and problem solving.
Sourcing and supplying equipment, systems, materials, technologies, and spare parts from qualified manufacturers and suppliers to meet project and operational requirements.
Delivering professional training, technical workshops, and tailored capacity-building programmes to develop skills, strengthen organisational capabilities, and support knowledge transfer.
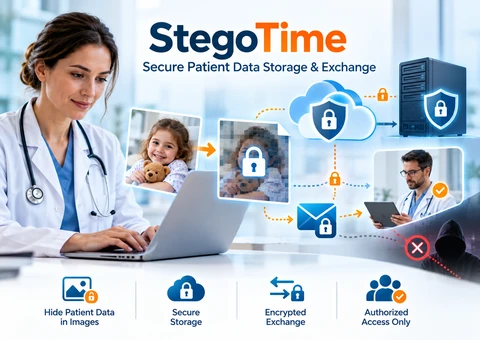
StegoTime provides an excellent, simple, flexible solution to protect your patient data, while it is stored on your computer, local server, or cloud; or while it is exchanged across the Internet. Simpley, use Stegotime to hide the patient data in an image of your choice (e.g., your patient photo), authroize your patient or any other person who is legally authroized to access this data, and store it or send it to them by email. You can be sure that no one can disclose the data except you, your paient, and those whom you authroized. As a doctor you have an ethical, legal and contractual duty to protect patient confidentiality. Under data protection law, those responsible for patient data are legally obliged to store it securely and protect it from unauthorized or unlawful processing. The General Medical Council (GMC) guidance on confidentiality states that “you must make sure any personal information about patients that you hold or control is effectively protected at all times against improper access, disclosure or loss”. You must make sure that identifiable patient data is not improperly disclosed in any circumstances. An inadvertent breach of patient confidentiality could result in you facing patient complaints or even a trust disciplinary or GMC investigation. Communicating via Mobile Apps NHS guidance for doctors using mobile apps which lack proper security features – such as WhatsApp – advises that “it should never be used for the sending of information in the professional healthcare environment.” The guidance warns that, as a consumer service, WhatsApp “does not have a service level agreement (SLA) with users and has no relevant data security certification” and, as such, should not be used to send patient information or details of clinical cases to colleagues. Data Storage on Portable Devices When used with care, portable storage devices are a valuable and convenient way to store and transfer data. However, since mobile devices are particularly vulnerable to loss or theft, security and best practice should be your first priority. Avoid storing identifiable personal data on personal mobile devices, such as memory sticks, laptops or personal mobile phones, which risk being misplaced or accessed by other people. Familiarise yourself with your trust's information security policy and the name of the person in charge of data security. Always follow trust procedures on the use of mobile devices, laptops and portable data storage. If you are worried about whether you should use a portable storage device at work, talk to your trust information officer for advice. Encryption and password protection of data held on mobile devices would be considered to be standard practice. Make sure you only transfer or store information in line with your trust's information security policies, and take care not to mix professional and personal data. There can be particular dangers where doctors use the same devices for both professional and personal use. Follow relevant GMC and NHS guidance and get to know your legal requirements under data protection law. If you lose any data, report the incident to the nominated senior person in your organisation immediately. They can then take appropriate action and inform patients, if necessary.
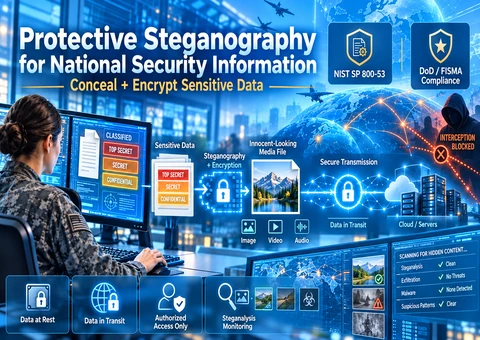
Department of Defense Applications of Steganography The U.S. Department of Defense (DoD) is mandated to follow the National Institute of Standards and Technology (NIST) Special Publication (SP) 800–53 to be compliant with the Federal Information Security Management Act (FISMA) of 2002, in which the most current version, Revision 4, serves as a Risk Management Framework (RMF) which contains a list of over eight-hundred unique security controls that federal organizations are required to implement to varying degrees depending on the risk categorization of their particular information system. There are several other NIST and DoD publications that complement the SP 800–53, however, this publication is the sole reference source for NIST security controls. With NIST’s SP 800–53 revision 4, it specifically addressed for the first time ever the dangerous threat of steganography. Specifically, the SC-7 boundary control security control, addresses monitoring for steganography; the malicious code protection security control, SI-3, addresses malicious code possibly hidden in files using steganography; and the SI-4 enhancement (18), addresses covert means that can be used for unauthorized exfiltration of organizational information. The U.S. Department of Defense (DoD) is mandated to incorporate digital steganography to protect National Security Information (NSI). It makes practical sense to apply a high level of security as is both feasible and possible on National Security Information (NSI) due to the fact that if this sensitive information were to come into the possession of adversaries, it could potentially cause grave damage to U.S. national security. It is logical then to apply the strongest forms of security controls to protect this information. One advantage of steganography is that it allows users to both cloak and encrypt data into cover mediums such as images, video and audio files, voice over Internet Protocol (VoIP) data, and many other types of digital media. In order for it to be effectively used, the NSI data could be hidden using steganography while the data is at rest, but especially when the data is in transit across networks. When NSI data is being copied to any type of media, it is required to be encrypted but could also be hidden using steganography. The added protection would make it so much more difficult for adversaries to locate NSI data, and if it were somehow spotted they would need to find the appropriate steganography application to attempt to open the file with the correct passphrase and crack the encryption. There would be a learning curve that would need to occur for all federal employees, military personnel, and DoD contractors who have access to NSI data in order to properly educate personnel on how use steganography applications and proper encryption methods and passphrase creation. However, this slight measure of pain would ensure that America’s most sensitive information is well-protected and if it were intercepted by adversaries, it would be nearly impossible for an adversary to read it. National Security Information (NSI), also known as classified information, as defined by Executive Order 12356 as being classified at three different levels as either top secret, secret, or confidential information that could be expected to cause gravedamage, serious damage, or a level of damage to national security respectively. Ronald Reagan, Executive Order 12356, 2nd April 1982. Intelligence Community Applications of Steganography The Intelligence Community uses cryptography almost by default to protect sensitive NSI. Cryptography systems are generally either symmetric with a single key or asymmetric with both public and private keys for decrypting messages. When encryption is employed in messages or data it raises suspicion by adversaries who could potentially be remotely monitoring network data packets and it’s a dead giveaway that at least some type of sensitive information is included within packets. Using cryptography openly may serve to compel adversaries to try even harder to decipher encrypted data. However, steganography is not detectable and does not raise suspicion unless it is specifically being checked for with special steganalysis software application tools and even then it is possible that if discovered, the secret message stego file will not be able to be decrypted and readable. Advanced Persistent Threat (APT) groups are often named by a numerical value and sometimes also associated with the name the malware the group uses. The “Stuxnet” virus was by far the most sophisticated digital warfare weapon ever conceived and has been confirmed by President Obama to have been developed cooperatively between the U.S. and Israel to thwart the Iranian efforts to enrich Uranium for nuclear weapon manufacturing. While steganography was not discovered within the complex bundles of code used in the Stuxnet virus, other forms of malware have incorporated steganography into the code to mask the exfiltration of sensitive proprietary, classified, personal and financial data. U.S. officials discovered that in 2010 a Russian spy ring located in the U.S. was utilizing “Duqu” and “Alureon” malware to exfiltrate classified U.S. NSI back to Russia using steganographic techniques to hide their payloads (Wendzel et al., 2014, p. 2). It is relatively safe to assume that government spy agencies like the National Security Agency (NSA) and the Central Intelligence Agency (CIA) have also used digital steganography by this point in time. Predictable Adversarial Response to Protective Steganography Use If a country such as the U.S. were to begin utilizing digital steganography to protect NSI, assuming it is not already doing so, the predictable adversarial response would be an increase in steganalysis tools designed to detect steganography file signatures combined with cryptanalytic software tools designed to break and decrypt encrypted data. State and non-State actors would also begin utilizing steganography if it was not already being employed to protect their own sensitive information. Essentially, the use of steganography will only result in nuclear détente situation that serves to elevate the level of sophistication that nations will have to ascend to in order to protect their NSI. In other words, if every country has nukes or uses digital steganography to protect NSI, then there is little value in having or using these types of weapons. Employing digital steganography combined with strong encryption does not assure secrecy any more than employing highly-compensated cybersecurity professionals does not assure an organization will never be hacked. What it does do, however, is make it much more difficult for adversaries to intercept and decrypt secret messages. For that reason, it does make practical sense for the U.S. government to implement some measure of “protective” steganography to better protect its most sensitive data. Conclusion In conclusion, digital steganography can be a very effective and affordable means of further protecting NSI beyond traditional encryption methods to conceal its existence altogether. It may not be worth training the massive amounts of U.S. government, military, and contractor personnel on how to properly use steganography applications to hide data in transit, but perhaps the cost and hassle would be justified only for Top Secret-level or above NSI. There is absolutely no reason that digital steganography has to only be used by the malicious actors online. There is a valid case to be made for the U.S. government to direct the implementation of digital steganography combined with strong encryption and passphrases to further protect its most sensitive information. It is all but guaranteed that America’s adversaries like Russia, China, Iran, and North Korea have implemented digital steganography into their cyber weapon arsenal, and perhaps the U.S. has secretly done so as well. If the U.S. has incorporated digital steganography to protect NSI then it is on the right track, however, if it has not then it is walking a dangerous line by not utilizing this great form of protection. Source: Using Digital Steganography to Protect National Security Information by z3roTrust, Nov 26, 2018